There is no evidence that hackers took control of South Africa’s air-traffic-control system. What is confirmed is more specific: malware reached an operational-technology environment connected to aviation services.
South Africa’s Air-Traffic Agency Found Malware in Operational Technology.
South Africa’s Air Traffic and Navigation Services detected suspicious activity and ransomware-linked malware in operational technology supporting weather-related air-traffic services. The malware was contained, but investigators are still examining the intrusion source, possible data exfiltration and operational impact.
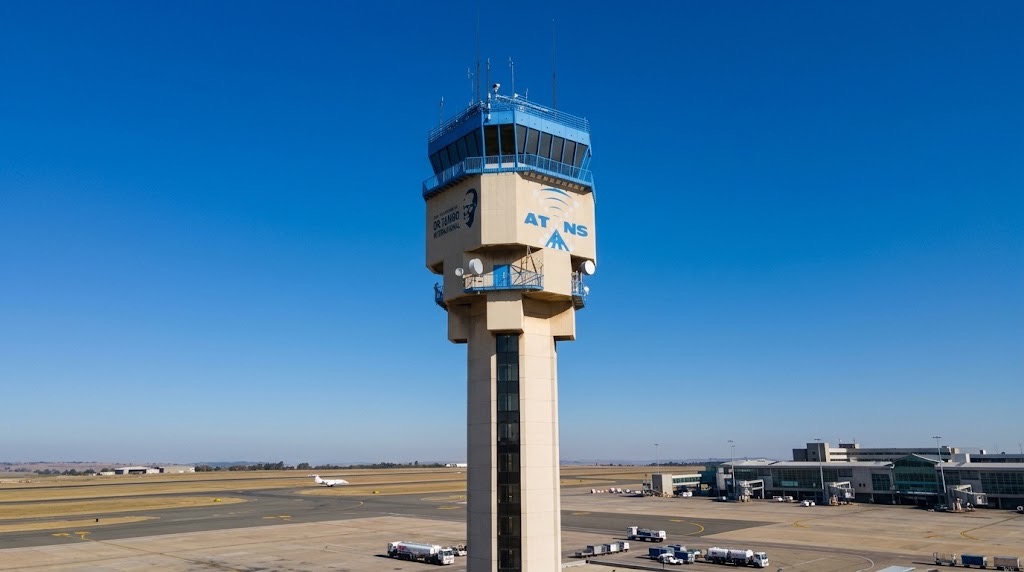
South Africa’s air-navigation provider is investigating malware discovered inside an operational-technology environment supporting weather-related air-traffic services, bringing cybersecurity unusually close to systems involved in real-world aviation operations.
The incident does not mean hackers took control of aircraft, radar or South Africa’s air-traffic-control system. But documents published by Air Traffic and Navigation Services, or ATNS, show why the investigation is more consequential than a conventional ransomware incident affecting office computers.
ATNS said monitoring systems detected suspicious activity inside operational technology, or OT, supporting weather services used by Air Traffic Services. Preliminary analysis identified malware commonly associated with the early stages of ransomware attacks.
Why operational technology changes the risk
Operational technology refers broadly to computerised systems that monitor or interact with physical processes. The US National Institute of Standards and Technology includes transportation infrastructure and industrial control systems among its examples.
Unlike ordinary corporate IT, where a compromised laptop may primarily expose files or credentials, OT environments can support processes where availability, integrity and safety matter as much as confidentiality. In ATNS’s case, the affected environment supported weather-related aviation services.
Pilots and air-traffic controllers depend on information about visibility, storms, wind and other conditions when planning and operating flights. South Africa’s Weather Service lists aviation forecasts and warnings among the information supplied to airlines, airports and controllers.
That makes the important question not simply whether malware entered the network, but whether it affected the availability or reliability of information used during operations.
ATNS has not said that it did. Its forensic investigation is specifically tasked with determining any impact on operational continuity and safety-critical services.
This is not yet a confirmed ransomware deployment
Some reports have described the incident as a ransomware attack, but ATNS’s own documentation is more cautious. It says investigators found malware “commonly associated with the early stages of ransomware attacks.” Technical teams subsequently contained the incident and removed malware.
That establishes the presence of ransomware-linked malware, but not that attackers successfully encrypted the OT environment or completed a ransomware operation. Investigators are still examining the infection source, attack vector, affected systems and any remaining risks.
Possible data theft is also being investigated
ATNS says network monitoring indicated possible data exfiltration to external IP addresses located in China.
That does not establish who conducted the intrusion. Attackers routinely use rented, compromised or intermediary infrastructure that can obscure their actual location.
The relevant question is whether information actually left ATNS systems and, if so, what was taken.
That distinction matters in the same way TechView Africa found when examining data-breach rights across six African countries: a security incident and a confirmed data breach are not automatically the same thing.
The alleged insider incident is separate
ATNS’s forensic procurement also covers allegations that employees at FAMM may have accessed or exfiltrated personal information without authorisation.
This should not be interpreted as evidence that an employee helped deploy the malware.
ATNS describes the matter as a separate alleged insider-threat and data-theft investigation and says its initial investigation could not substantiate the allegations. Independent investigators have been asked to examine access records, user activity and relevant systems.
Why the incident matters beyond aviation
The ATNS case illustrates a wider cybersecurity problem: the boundary between digital systems and physical infrastructure is increasingly thin.
When malware reaches systems connected to transport, electricity, water, manufacturing or other critical services, defenders have to think beyond stolen information. They also have to protect continuity, reliability and safe operation.
For ATNS, several decisive facts remain unresolved: the original intrusion path, whether data was actually exfiltrated, which systems were affected and whether any measurable operational impact occurred. Until those questions are answered, those limits belong in the story as prominently as the cyberattack itself.
Our Recommendation
Treat this as a significant operational-technology cybersecurity investigation, not evidence that hackers took over South African air traffic control.
The most important findings to watch are whether investigators confirm data exfiltration, identify the initial access route and establish whether aviation operations or safety-critical services experienced any measurable impact.
For critical-infrastructure operators, the case reinforces the need for dedicated OT asset visibility, network monitoring, segmentation, controlled administrative access and incident-response procedures designed around operational continuity.
Sources & Verification
ATNS — Digital forensic investigation tender and incident scope
Business Day — Air traffic agency probes cyberattack
NIST — Guide to Operational Technology Security
Frequently asked questions
Was South Africa’s air-traffic-control system hacked?
ATNS confirmed malware inside operational technology supporting weather-related air-traffic services. There is no public evidence that attackers took control of the broader air-traffic-control system.
Was this definitely a ransomware attack?
Not yet. ATNS says malware associated with the early stages of ransomware attacks was found, but the full attack sequence remains under investigation.
Was data stolen from ATNS?
Possibly, but this has not been confirmed. Investigators are examining indications of possible data exfiltration.
Were ATNS employees involved?
There is no established evidence of that. The alleged insider-data incident is a separate investigation, and ATNS says its initial inquiry did not substantiate the allegations.
Apple TV Arrives in Nigeria Through a ₦1,300 iCloud+ Bundle

Want to Buy Dangote Refinery Shares at ₦525? Here’s Where and How
Dangote Refinery IPO Gets SEC Approval at ₦525 Per Share
Nvidia Already Dominates AI Chips. Now It’s Buying Hugging Face for $12.9 Billion
Why Data Centres Are Becoming One of Africa’s Most Important AI Stories
Nigeria Wants More Electric Vehicles But Where Will Drivers Charge Them?
How to Apply for Builders Festival ’26: Build Your Case Around One Institutional Problem
Follow TechView Africa on WhatsApp
Get TechView Africa updates on WhatsApp. Follow our channel for practical technology news, product guides and digital trends from Nigeria and across Africa.
Leave a comment
Comments cannot be edited or deleted after posting. Please review your comment before submitting.
No comments yet. Start the conversation.